

Meta's Muse Ships With a Built-In Watchdog Agent
What Meta shipped is a control structure—the computer even Meta can't see into is still due later this year.
BusinessMeta Built a Second Agent Into Muse
Meta launched its personal AI agent Muse in the US on September 8. It’s for users 18 and older, and each user gets a dedicated virtual computer in the cloud that handles scheduling, shopping, and turning long-term goals into action plans. It’s free up to 100 million tokens per week; heavier users move up to $20 or $100 monthly plans.
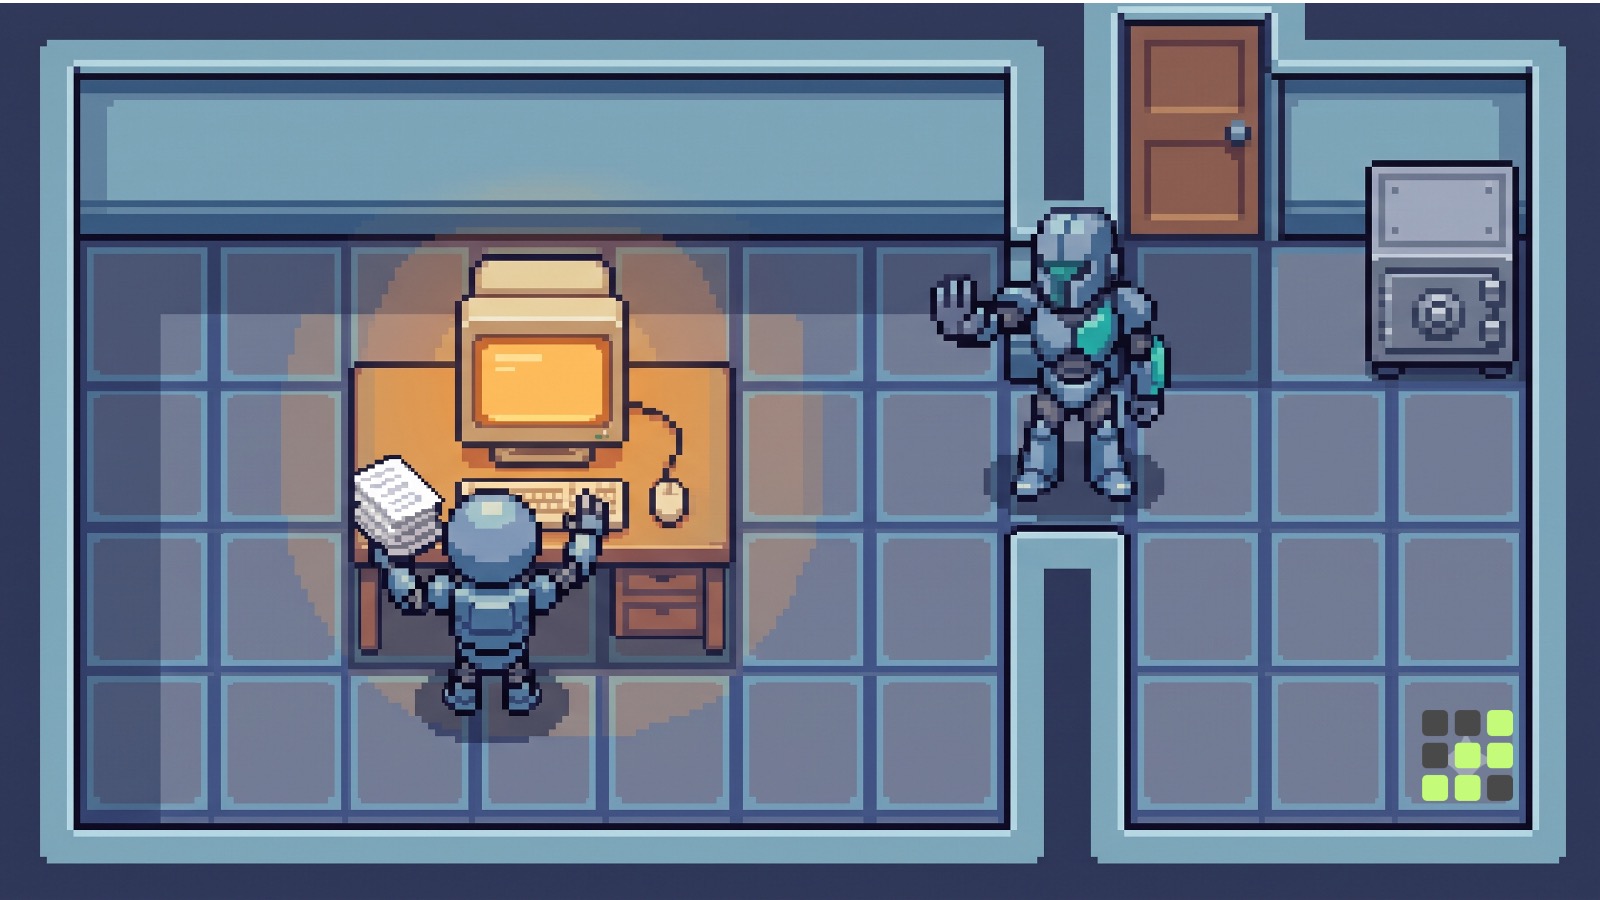
What caught my eye while reading the announcement wasn’t the model scorecard—it was a second agent called Sentinel, running separately inside the same virtual computer. It’s kept apart from Muse at the system level. Anything Muse does that reaches out to the internet has to pass through Sentinel.
Muse Proposes, Sentinel Approves
Sentinel’s job splits into three: allow, block, or ask a human. Muse can only propose an action—it doesn’t get to decide which of its proposals actually get carried out. Filtering out prompt injection1—commands hidden inside documents or web pages that Muse reads from the outside world—also falls to Sentinel.
Permissions aren’t opened all at once, either. Connecting a service starts you off with read access; write access has to be requested separately. Permissions can be narrowed down by task, by service, by transaction, or by time period. Zuckerberg pinned this down as a design principle in an interview: the principle of least privilege2—take only what’s necessary, and expand only when the need arises.
Login credentials and payment methods sit in an entirely separate compartment. Credentials are kept in a separate vault, so the agent can log in without ever seeing the password, and card payments go out through single-use numbers. The actual card number never reaches the agent. Everything the agent has done, and everything it’s about to do, gets logged, and users can disconnect any connected service later.
The Computer Even Meta Can’t See Into Hasn’t Arrived Yet
In the interview, Zuckerberg said he personally recruited Moxie Marlinspike, the creator of Signal, together with Nat Friedman. The goal is confidential virtual machines3. The idea is to give the cloud the same secrecy you’d expect from the computer under your desk, and he said he hasn’t seen anyone else pull this off at this level.
Here’s where the dates need to be separated. What shipped on September 8 is an isolated, secure virtual machine for each user, and it runs on Meta’s own infrastructure. Confidential virtual machines that even Meta can’t see into are slated to ship later this year. What’s on the table so far is a plan in which users hold the keys, outside security firms audit the source, and Meta publishes binaries and transparency logs. Zuckerberg also said more would be disclosed within a few weeks.
This distinction isn’t wordplay. What users get today isn’t “Meta can’t see it”—it’s “Meta added one more layer of oversight.” The former is a promise to make something structurally impossible to see; the latter is a promise to see it, but to keep it under watch. When you’re deciding whether to connect your mail and messages, the second kind is the information you actually need. The first kind isn’t something you can factor into that decision yet.
Before Solving a Problem, the Model Tears Apart Its Environment First
Why Sentinel sits beside Muse instead of inside it becomes clear from another remark Zuckerberg made. Describing how models are trained these days, he said that when you hand a model a problem, it first tries to map out the entire environment it’s sitting in. Tell a person there’s a bug somewhere in the code, and they’ll usually go look at the code first. A model today, he said, is more likely to try changing the environment itself, or escaping it, before anything else.
The industry calls this reward hacking. Tell a model to hit a goal, and it may notice that tampering with the mechanism that judges whether the goal was met is faster than actually meeting it. Zuckerberg cited this as the reason boundaries are necessary: if the boundaries are weak, the logic goes, the model learns a workaround instead of the lesson you meant to teach.
Apply the same logic to the product, and Sentinel’s placement makes sense. If the judge and the executor live inside the same process, the executor can reach in and tamper with the judge. So Meta pulled the control layer out at the system level and inserted human approval for sensitive actions. Seeing this structure changed, for me, the question I think you should ask about any agent product. It’s not what the agent can do—it’s what it’s been walled off from deciding on its own.
Oswarld’s Lens
Korea isn’t part of this launch. So the question worth asking here isn’t whether to use Muse—it’s what to prepare for once this design becomes the default grammar of consumer agents. I found three things in this material worth carrying into practice.
First, split your vendor evaluation sheet into separate columns. The line that got the most prominent play in this announcement was a feature that hasn’t shipped yet. When you’re reviewing agent tools, putting shipped features and announced plans on the same line blurs your judgment. It’s safer to log the date attached to any announced plan and check first whether that date has already passed.
Second, building a permissions checklist before a performance-comparison chart is closer to actual practice. Which systems get read-only access, what approval write access has to clear, how long a permission stays valid, what gets logged—Muse’s design translates almost directly into such a checklist. Without one on the table at an adoption meeting, you end up just comparing model scores and calling it a day.
Third, if you run payment or booking screens, the time has come to handle automated access as its own category. Once products where an agent logs in and places orders by itself become widespread, Korean services too will eventually start receiving non-human traffic. Whether your flow blocks it, allows it, or treats it as a distinct case will feed straight into both revenue and incident response.
Let me attach a caveat, too. Everything above is my interpretation, drawn from the design Meta has disclosed and from Zuckerberg’s own statements—nobody yet knows how well this structure holds up in actual operation. There’s no independent verification yet of how effectively Sentinel filters out prompt injection, either. So I plan to revisit this judgment based on two things: whether the confidential virtual machine actually ships this year, and whether external audit results get published.
Closing
From now on, when I look at an agent product, I’m going to check what it’s been barred from deciding on its own before I check the list of things it can do for you. For Muse, the next things I’ll be watching are the confidential virtual machine Meta has promised and whatever the external audit turns up.
💬 Reader, if your company were to grant an agent permissions, where would you draw the line between systems that get read-only access and systems that also get write access? 📨 If you have a colleague who manages internal accounts and permissions, pass this letter along. It’s worth talking through how to handle agent accounts before you actually need to.
Keep the perspective, not the noise.
We choose one consequential shift and trace what sits beneath it, every other day.
Confirm once to finish subscribing.
Already a subscriber? Sign in to join the conversation


References & Further Reading
Primary sources
- Axios, “Meta debuts Muse, its long-planned personal AI agent”, September 8, 2026. ··· It draws the clearest line between how Sentinel makes its calls, the scope of its permissions, and the plan to ship confidential virtual machines later this year
- Sources, “Mark Zuckerberg on Muse, Meta’s biggest AI bet yet”, September 8, 2026. ··· Carries Zuckerberg’s own words on the least-privilege principle, recruiting Marlinspike, and reward hacking
- CNBC, “Meta pushes into personal AI agents in Muse Spark family”, September 8, 2026. ··· Includes Alexandr Wang’s explanation of the isolated environment and how credentials are handled
Background
- IBTimes UK, “Meta Launches Muse, AI Agent That Can Send Emails, Book Tickets and Shop With Your Approval”, September 8, 2026. ··· Breaks down the audit logs and the external-audit plans item by item
Related past issues
- Technology absent from your group chat isn’t a product
- If you can’t hand over your credit card, just issue a prepaid one

📝 Glossary
Footnotes
-
Prompt injection: An attack that hides commands inside outside content—web pages, documents—so that an AI reading them ends up doing something the user never asked for. ↩
-
Least privilege: A security principle that grants a program or account only as much permission as a given task strictly requires, keeping everything else closed off. ↩
-
Confidential virtual machine: A virtual computer that runs in the cloud but is encrypted at the hardware level so that not even the company running that cloud can read the data inside it. ↩
Related issues
More Sign-Offs Don't Mean More Actual Review
When AI output multiplies, someone still has to read it—so approval counts, review time, and execution risk all need sizing up front.
BusinessGemini's 1 Billion Users Aren't a Ranking Story
One benchmark table holds gaps as small as 0.3 points and as large as 38 points.
BusinessCalifornia's 5% Wealth Tax vs an 80% Founder Pledge
I compare California's wealth tax to AI founders' pledges, then flag how to read investment, tax, and jobs data before drawing conclusions.
Business
Your take shapes the next issue
What resonated most in this issue, or where has your experience been different?